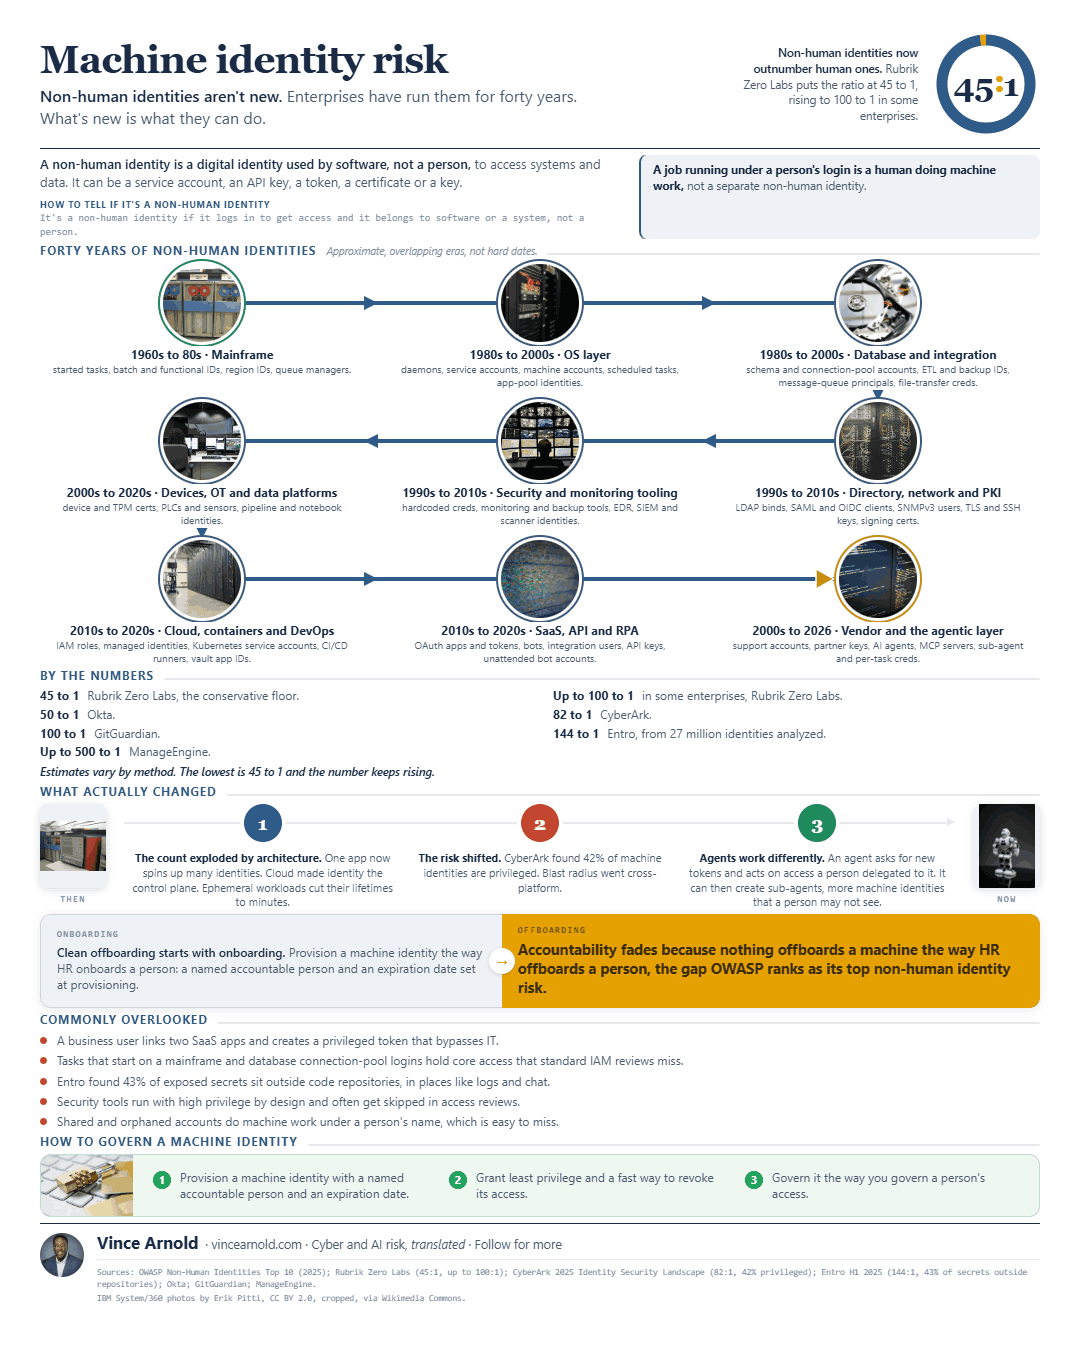
In most companies, people are now the minority. By Rubrik Zero Labs’ count, machine identities outnumber human users 45 to 1, reaching 100 to 1 in some environments. Most are service accounts and AI agents working across your systems daily.
Identity controls were built for people, not machines. A person has a manager and a termination date. A machine identity usually has neither. So its access persists long after its purpose has ended.
For people, provisioning assumes a human is present. Someone authenticates at login. Someone files the deprovisioning request when a worker leaves. A machine identity breaks both assumptions. It authenticates without a human present. Teams rarely deprovision it.
When a machine identity is misused, the first question is who’s accountable for it. Usually it’s a team, not a named person.
Here’s the fix: routine identity hygiene. When you provision a machine identity, assign a named accountable person and an expiration date. Grant least privilege and a fast way to revoke its access. Deprovision it when its purpose ends, the same way you deprovision a person.
Hold machine identities to the provisioning and deprovisioning discipline you already apply to people.
Who is the named person behind the agents you already run?
Source:Rubrik Zero Labs