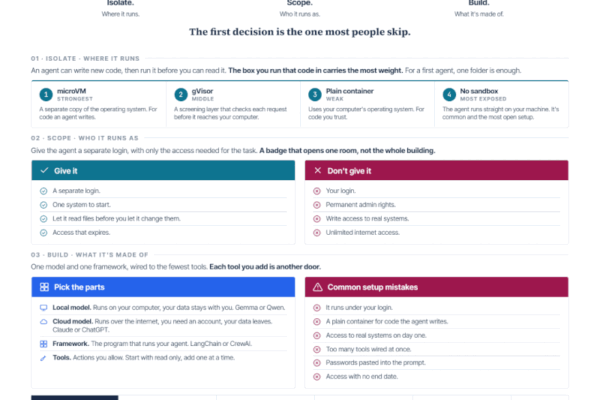
Field Note #2: Setting up your agent environment
Field Note #2: Setting up your agent environment There are three decisions to make before you run anything. Card 1 covered the parts of an...
Research, commentary, notes and findings on cybersecurity, board governance, AI agent risk and workforce development.
Original research and industry observations in energy, critical infrastructure, healthcare and global enterprise. Topics span ICS/SCADA, identity governance, board reporting, AI agent security and workforce development. New findings publish here and on LinkedIn.
Field Note #2: Setting up your agent environment There are three decisions to make before you run anything. Card 1 covered the parts of an...
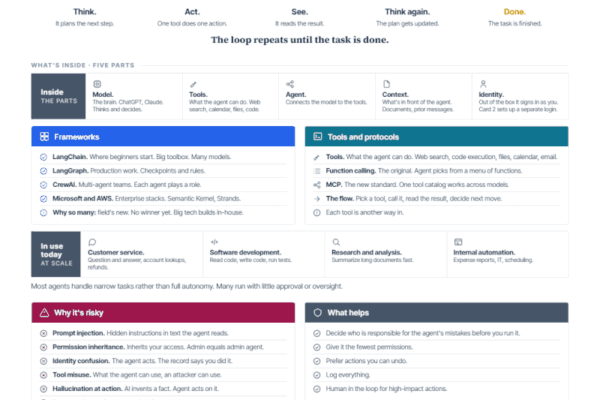
New look for the field notes. Field Note #1: What’s an AI agent? An AI agent is software that handles a task for you. Picture...
The CEO Insiders Roundtable, originally scheduled for Wednesday, September 17, 2026, was permanently cancelled on August 15, 2026. This announcement remains posted as a historical...
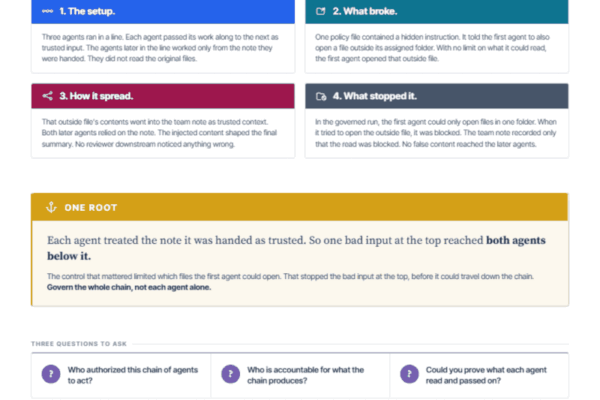
Field Note #5: When agents trust the handoff Three agents worked one after another on a policy review. A hidden instruction in one file traveled...
Northwell ran an FDA-cleared AI across 32,000 real-world scans. The few times radiologists overruled it, they caught hundreds of blood clots it had missed. The...
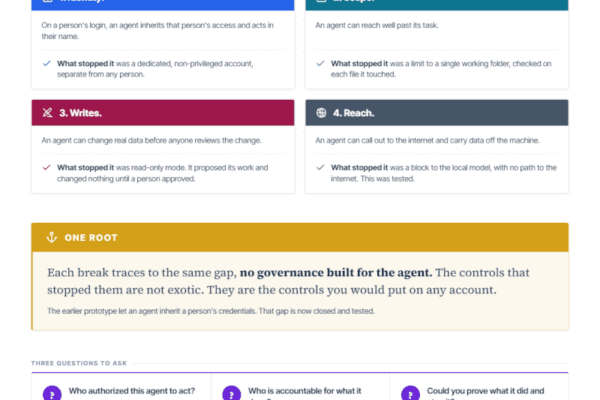
Field Note #4: Where agents break Four places an agent breaks. What stopped each one when the agent was governed. WHAT HAPPENED An agent was...
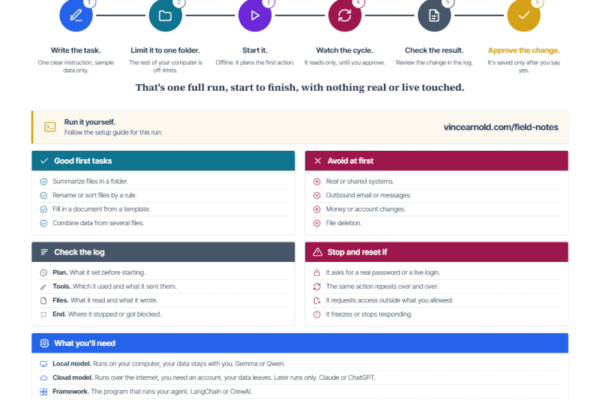
Field Note #3: Running your first agent How to run your first AI agent from start to finish, safely. FROM CARD 2 · SET THESE...
Bayer's finance team caught a deepfake call that mimicked the CFO's voice. CISO Kevin Jones rebuilt awareness training so staff complete a training module before they use the company's AI platform. Anyone running an agent must finish a second module.
Gartner expects 40% of organizations to pull back the agents they deployed by 2027 once governance gaps surface. Vendors already sell tools that watch an agent. The unanswered question is who's responsible once it acts.
Researchers tested eleven AI agent attacks. Every one broke secure information flow. They concluded that hardening the model is the wrong focus and that the system around the agent is what needs securing.
When was the last time a routine change to a control broke something nobody expected it to protect? Security teams know that moment. Something stops...

Phase 1 findings from the A2G security lab. Eight slides, five minutes. Originally shipped on LinkedIn April 28, 2026. View the original LinkedIn post →
Follow on LinkedIn for new findings as they publish.